A Jackson, Mississippi web hosting company has cut off a client of more than 15 years, just days after a cyberattack knocked his website offline for more than a week. The client, Dennis Fett, runs what he describes as a global peacock information center, a niche business he has operated for three decades. According to WLBT, which first reported the story on October 15, 2026, the hosting provider, U.S.NEXT, told Fett to find a new web host rather than restoring the service that had carried his business online since before many modern cloud platforms existed.
The episode has become one of the more closely watched small-business cybersecurity stories of the week, picked up by outlets including WTVA, Inc.com, Yahoo Tech, The Record from Recorded Future News, The Cool Down, and cedarnews.net. It captures a problem that rarely gets headline treatment: what happens to a small, loyal customer when the vendor they depend on gets breached and decides the cleanup is not worth the relationship.
Industry insights, the latest tech news, and special interviews, all in the Tech Insider Newsletter.
One email a week. No spam, unsubscribe anytime.
Don't miss new tech stories on Google
Add Tech Insider once in the Google app and our stories appear in your news suggestions.
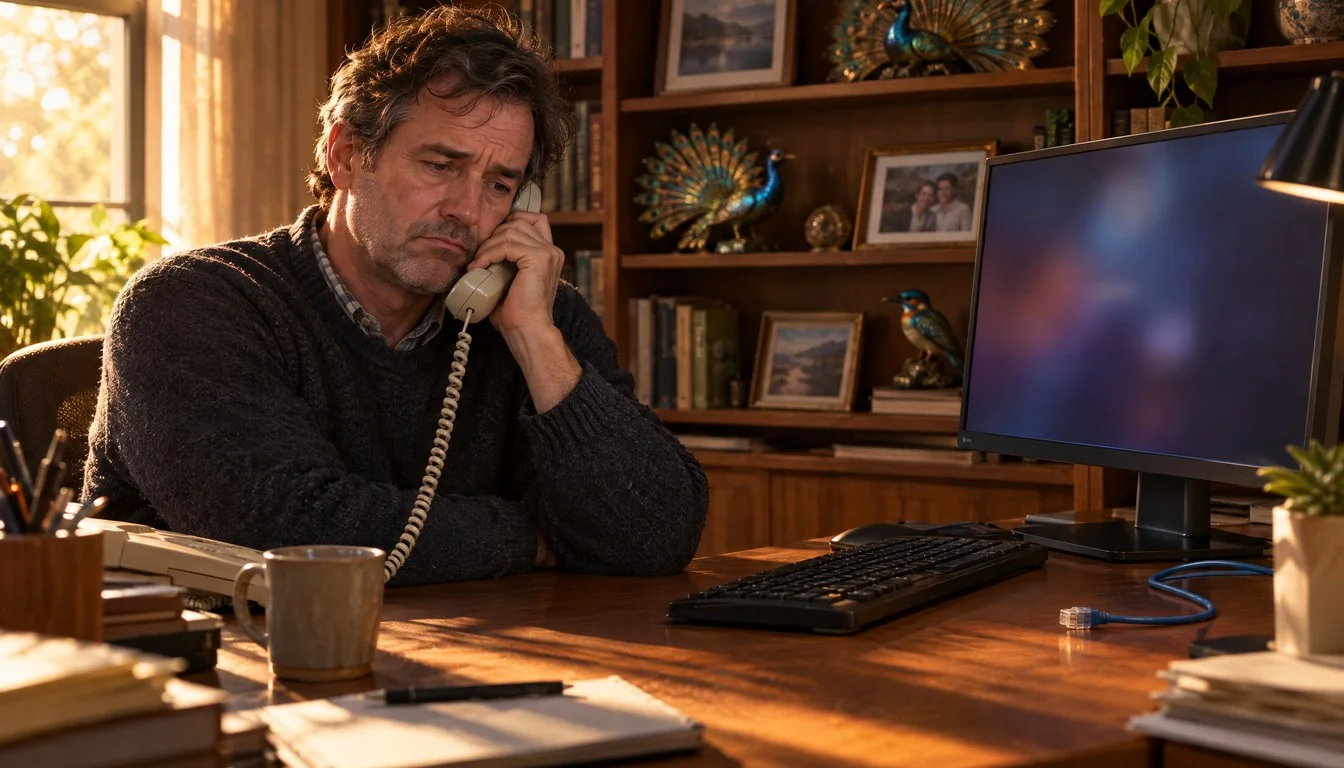
Dennis Fett had hosted his site with U.S.NEXT for what he called “15 plus years.” That is longer than most web hosting companies have existed in their current form, and longer than most small-business owners stay with any single vendor for anything. The relationship ended not with a renewal notice or a migration plan, but with a phone call from the company’s owner telling Fett his services would not be restored.
“I was kind of left hanging here in limbo for eight days, and then the first phone call I get is to tell me they’re not going to provide my web services anymore after 15 plus years.”
Fett’s business is not a tech company or an e-commerce giant. It is a specialized information service built around peacocks, a niche audience he has served for roughly 30 years, with the web presence underpinning orders and consulting work. For a business that size, the web host is not a line item. It is the storefront, the inbox, and the record of who ordered what and when. U.S.NEXT’s decision to walk away after the breach left that storefront with no owner and no clear path forward, at least for the moment.
The attack on U.S.NEXT’s systems occurred on October 8, 2026. What followed was an outage that stretched across eight days, according to the reporting that first surfaced the story. During that window, Fett’s website and the email tied to his hosting account were unreachable, which meant any incoming orders, consulting requests, or customer messages sent to his address during the outage simply would not arrive.
U.S.NEXT has not responded to a request from WLBT for an explanation of what happened or why it chose to end the relationship rather than restore service. That silence is notable, because it leaves several basic questions unanswered: what kind of attack hit the company’s infrastructure, whether customer data beyond uptime was affected, and how many other clients besides Fett lost service or lost their host entirely. None of those details are confirmed publicly as of this writing, and any reporting that fills in those gaps should be read as provisional until the company speaks on the record.
Laying out the sequence of events helps explain why this story resonated beyond Mississippi. It is a compact, almost textbook case of how a vendor-side cybersecurity incident cascades into real financial harm for a downstream small business, and then compounds that harm with an abrupt loss of service.
Every row above traces back to Fett’s own account of events as reported by WLBT and WTVA. The attack method, the identity of whoever carried it out, whether the incident involved ransomware, and the total number of U.S.NEXT clients affected all remain unconfirmed. Readers should treat any claim about those specifics, wherever they appear online, with caution until U.S.NEXT or an investigating authority confirms them.
Fett’s business is unusual by tech-industry standards precisely because it is so far removed from tech. His global peacock information center has operated for about 30 years, built on accumulated expertise rather than venture funding or a product roadmap. The website functioned as the primary channel for both sales and consulting inquiries, the kind of operation where a missed email can mean a missed sale that never gets a second chance.
“My business is now dead in the water.”
That phrase captures something easy to overlook in cybersecurity coverage focused on nine-figure breaches and nation-state actors: for a one-person or family-run operation, an eight-day outage is not a line in a quarterly risk report. It is the entire operation stalling out. Multiply Fett’s situation across however many other small clients U.S.NEXT serves, and the real cost of this incident is not measured only in the company’s own recovery bill, but in the compounding disruption pushed onto customers who had no say in U.S.NEXT’s security posture and no backup plan of their own.
U.S.NEXT’s lack of public comment stands out against a backdrop where regulators and security researchers increasingly expect breached companies to disclose basics quickly: what was affected, what wasn’t, and what customers should do. Even organizations that eventually communicate well often stumble in the first days of an incident. The gap between attack and disclosure has become its own research subject, and the pattern of extended, uncommunicative outages is not unique to a small Jackson-based host.
Our previous coverage of a ransomware attack on Japan’s IDCF Cloud, which took down services for 495 clients, showed a similar dynamic: a hosting or cloud provider absorbs an attack, and the business customers downstream absorb the consequences with limited visibility into what is actually happening to their data and their uptime. In that case, as in U.S.NEXT’s, the provider’s internal timeline for root-cause analysis and recovery ran far longer than most small-business customers could tolerate without a contingency plan.
From the outside, ending a 15-year customer relationship immediately after that customer suffered an outage looks punitive. But there are a few plausible, if unconfirmed, reasons a smaller regional host might take this path after an attack. Rebuilding compromised infrastructure selectively for some accounts while discontinuing others can be a way to shrink the restoration workload during an active incident response. It can also reflect a provider deciding to exit certain hosting tiers or legacy environments entirely rather than rebuild them post-breach, especially if those environments ran on older infrastructure that contributed to the exposure in the first place.
None of those explanations have been confirmed by U.S.NEXT, and the company’s silence means the public record currently consists only of Fett’s experience: an outage, then a termination call, with no stated reason attached. For a small-business owner, the distinction between “we can’t restore your account” and “we are choosing not to” matters enormously, and it is exactly the kind of detail a company protects itself by clarifying quickly rather than leaving to speculation.
The U.S.NEXT incident is small in scale next to some of the year’s larger infrastructure breaches, but it sits inside a recognizable pattern of hosting and cloud-dependency risk that has shown up repeatedly in 2026 reporting. The table below places the known facts of the Jackson case alongside other previously reported hosting, cloud, and SMB-security incidents for scale.
What stands out when the Jackson case is set next to these is not its size, but how closely it mirrors the mechanics researchers describe at every scale: an attack disrupts the host, downstream customers lose access for days rather than hours, and the aftermath is dictated by a vendor’s internal recovery priorities rather than the customer’s business needs. A separate analysis we covered found that cyberattacks can cost affected firms roughly 15% of annual revenue once downtime, recovery, and lost business are totaled, a figure that tracks uncomfortably well with what an eight-day shutdown could mean for a business the size of Fett’s.
Fett’s situation is a case study in third-party risk, a concept usually discussed in the context of enterprise supply chains but equally relevant to a one-person business running on a single hosting account. When a small business outsources its entire web and email presence to one vendor, it inherits that vendor’s security posture, incident-response speed, and business decisions about which customers to keep after a crisis. There is rarely a contract clause that protects the customer from “we are discontinuing your account,” especially with smaller regional providers operating outside the more rigid service-level agreements enterprise customers negotiate.
That asymmetry is why cybersecurity guidance aimed at small businesses increasingly treats hosting-provider resilience as part of basic security hygiene, not a separate IT concern. Our guide on protecting against ransomware covers practical steps, including maintaining offline backups of website content and customer records independent of a single hosting account, specifically so a provider-side incident doesn’t leave a business with zero options the way it did for Fett during his eight days offline.
Stories like this one carry a reputational cost that extends beyond the single company involved. Small-business owners researching hosting providers increasingly search for breach histories before signing up, and a widely syndicated story about a host dropping a 15-year client after an unexplained attack is the kind of result that shows up in exactly that research. For U.S.NEXT, the near-term market impact is likely to show up less in stock-price terms, since it is a privately held regional provider, and more in client retention and new-signup hesitation across the Mississippi small-business market it serves, including the government and nonprofit-adjacent customers the company has reportedly hosted in the past.
More broadly, the incident adds to a steady drumbeat of coverage suggesting that cyberattacks on smaller cybersecurity-adjacent infrastructure, not just marquee breaches at major corporations, are shaping how buyers evaluate vendors. A survey we covered found that 43% of UK firms reported being hit by a cyberattack in 2026, a figure that underscores how routine these events have become even as individual cases like Fett’s still generate outsized attention because of the human stakes involved.
Hosting-provider breaches are not a new category of incident, but 2026 has seen a steady stream of cases where the provider’s own infrastructure, rather than the end customer’s practices, became the point of failure. The IDCF Cloud ransomware incident in Japan left hundreds of clients without service while some storage zones were reported unrecoverable. Kiteworks told its own users to shut down servers proactively over fears of an imminent attack, a step that itself disrupted customer operations even before any breach was confirmed.
A separate write-up tracking the incident, published by Vertical Consulting, noted that the case has become a talking point among IT providers advising small-business clients on vendor dependency. What makes the U.S.NEXT case distinct within that pattern is the follow-through: most hosting-provider incidents end, eventually, with restored service and a postmortem. Fett’s case ended instead with termination, a resolution that leaves the underlying question of what caused the eight-day outage permanently unresolved from the customer’s side, since he no longer has a relationship with the company that could answer it.
Public statements directly tied to this specific incident remain limited to Fett’s own account, carried by WLBT and WTVA, and U.S.NEXT’s decision not to respond to media questions. That silence is itself a data point. In an environment where breach disclosure norms are tightening, a company’s choice to let a wronged 15-year customer do all the public talking, without offering its own account, tends to amplify scrutiny rather than reduce it.
“I was kind of left hanging here in limbo for eight days, and then the first phone call I get is to tell me they’re not going to provide my web services anymore after 15 plus years.”
That single quote, repeated across every outlet that picked up the story, has effectively become the incident’s defining statement, precisely because U.S.NEXT has not offered a competing or clarifying narrative to sit alongside it.
Not every provider facing a cyberattack responds the way U.S.NEXT reportedly did. The range of outcomes across recent incidents shows there is no single playbook, but there is a clear divide between providers that communicate proactively and those that leave customers to find out what happened through local news coverage.
For a business owner like Fett, the practical difference between these response patterns is enormous. A provider that communicates a timeline, even a bad one, gives a customer the information needed to decide whether to wait it out or move elsewhere. A provider that goes silent for eight days and then ends the relationship by phone leaves the customer with neither restored service nor the information needed to plan around the loss.
For other U.S.NEXT customers reading this story, and for small-business owners anywhere relying on a single regional hosting provider, there are a handful of concrete steps worth taking immediately rather than after the next outage. First, confirm whether your own hosting account was affected by contacting the provider directly rather than assuming silence means your service is unaffected. Second, export and store a current backup of website content, customer records, and email archives somewhere independent of the hosting account itself, whether that is a separate cloud storage service or a local backup.
Third, register a domain transfer or at least confirm who controls the domain registration separately from the hosting account, since losing access to a host should never also mean losing the domain name a business has built its identity around. These steps mirror the broader resilience guidance security researchers have pushed in the wake of similar incidents this year, including the lesson from the IDCF Cloud outage that some data, once lost at the provider level, simply cannot be recovered after the fact.
Several outcomes look plausible in the days and weeks ahead, based on how similar small-business cybersecurity stories have unfolded this year.
The U.S.NEXT story is unlikely to make any list of the year’s biggest breaches by record count or dollar figure. Its significance lies elsewhere: it is a plain illustration of how a cyberattack on a vendor can end a decade-and-a-half business relationship overnight, with no restoration, no clear explanation, and no guaranteed recourse for the customer left holding the loss. As cyberattacks on hosting and cloud infrastructure continue at the pace seen throughout 2026, from large multinational providers down to regional hosts serving a handful of small businesses, Fett’s experience is a reminder that the customer at the bottom of that chain usually has the least visibility and the fewest options when things go wrong.
What company was hacked in the U.S.NEXT cyberattack story?
U.S.NEXT, a Jackson, Mississippi-based web hosting company, suffered a cyberattack on October 8, 2026, according to WLBT and WTVA.
Who is Dennis Fett and why is his case notable?
Dennis Fett runs a global peacock information center that he has operated for about 30 years. He had hosted his website with U.S.NEXT for more than 15 years before the company ended the relationship following an eight-day outage tied to the attack.
How long was Dennis Fett’s website down?
His website and email were reported offline for eight days following the October 8, 2026 attack, according to his account to WLBT.
Did U.S.NEXT explain why it dropped the client?
No. U.S.NEXT did not respond to WLBT’s request for an explanation of the outage or the decision to end Fett’s service.
What type of cyberattack hit U.S.NEXT?
The exact attack method has not been confirmed publicly. Reports have not established whether the incident involved ransomware or another form of intrusion.
How many other U.S.NEXT customers were affected?
That figure has not been confirmed. Fett’s account is the one that has been detailed in reporting so far, and the full scope of affected clients remains unknown.
What should small businesses learn from this incident?
Security researchers generally recommend keeping backups of website and customer data independent of a single hosting provider, and confirming domain registration control separately from hosting, so a provider-side incident cannot eliminate every option at once.
Has Dennis Fett found a new web host?
That has not been confirmed in reporting as of October 16, 2026. His immediate priority, as described to WLBT, was finding a new host after being told U.S.NEXT would not restore his service.
Marcus Chen is a senior editor at Tech Insider, where he leads coverage of the US online gaming market, including sweepstakes and social casinos, alongside consumer technology. He evaluates operators on their published terms, licensing and RNG certifications, stated redemption policies, and corroborating independent reporting, and writes plainly about what the evidence supports. Tech Insider does not run first-party money tests and does not gamble with reader funds. Marcus has reported on the technology and online-gaming industries for more than a decade.
The Tech Insider Newsletter
Industry insights, the latest tech news, and special interviews, every week.
One email a week. No spam, unsubscribe anytime.
Tech Insider delivers in-depth coverage of the technologies shaping the future: AI, cybersecurity, cloud computing, hardware, and the trends that matter.
Tech Insider delivers in-depth coverage of the technologies shaping our future. From AI and cybersecurity to cloud computing and hardware innovation, our editorial team covers the trends that matter.
Tech Insider delivers in-depth coverage of the technologies shaping our future. From AI and cybersecurity to cloud computing and hardware innovation, our editorial team covers the trends that matter.
English | Svenska | Français | Suomi
We use cookies to measure traffic and improve Tech Insider. Read our Privacy Policy.
The Tech Insider Newsletter: industry insights, tech news, and special interviews.